Exercise the agent configuration before an attacker does. Sparring screens an agent's instructions, tools, and scope — and hands you the gap list, signed.
STEP 01
Pick the target
An agent bundle: system prompt, tool list, MCP servers, retrieval config. The tour runs the sample vulnerable bundle.
STEP 02
Eight layers of screening
Deterministic checks run across input, retrieval, guardrails, tool and agent security, output, and monitoring — including six red-team probes: injection, poisoned tool descriptions, MCP overreach, exfiltration instructions, hygiene. No model is queried and no payload is executed.
STEP 03
Tier + findings
The bundle tiers on the evidence: the vulnerable sample lands HIGH — 22 findings, each with severity, the evidence behind it, and its remediation, mapped to OWASP LLM/ASI and starter control crosswalks.
STEP 04
Signed pack, human triage
The run closes under a governed decision: findings wait for a named reviewer's triage, and the whole assessment is emitted as a signed evidence pack — verifiable offline.
Watch it run
The real assessment, stage by stage — the same engine the CLI runs, on the sample vulnerable bundle.
sparring · sample bundletokynd
# assess the sample (vulnerable) bundle
$ tokynd sparring assess --bundle samples/sparring/vulnerable_bundle.json --out ./sparring-out --signer "A. Reviewer"
8 layers screened · 6 red-team probes run
Tier: HIGH · score 36/37
22 findings — 2 critical · 13 high · 6 medium · 1 low
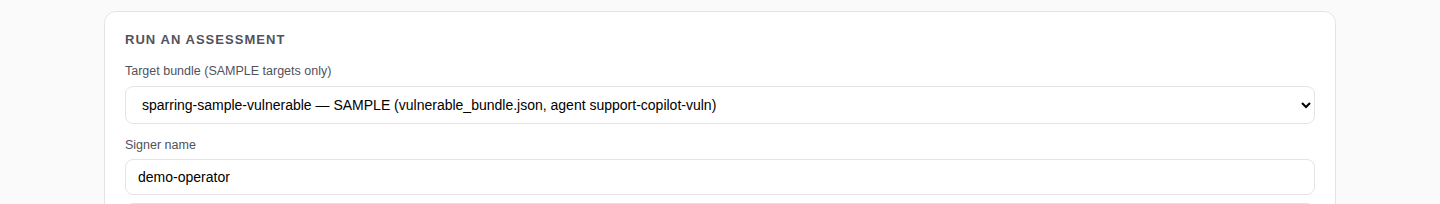
The Sparring assessment screen: pick a sample target bundle, name a signer, run.
Highsparring-sample-vulnerable
Tier high · 36/37 — 22 findings
Direct and indirect injection, tool-description poisoning, MCP overreach — the everything-server's shell and write scope — an exfiltration instruction, and missing hygiene controls. Each finding mapped to OWASP LLM/ASI and starter crosswalks (SOC 2, NIST, ISO/IEC 42001, EU AI Act).
Probes failed 6/6Findings 22
# verify the signed evidence pack — offline
$ tokynd sparring verify-pack ./sparring-out
OK — signature and pack integrity verified
✓
Human triage — findings are proposed until a named reviewer triages them
✓
Evidence — the signed pack — manifest, findings, decision — verifies with no Tokynd account